# Security
Our cybersecurity approach is proactive and multifaceted, grounded in best practices to anticipate and mitigate threats.
## Information Security Management
Based on global industry standards and best-practices, our cybersecurity program is implemented through training, design requirements, controls, testing, auditing, and more.
## Security by Design
We safeguard the **3D**EXPERIENCE platform through a standards-based secure software development lifecycle (SSDLC), robust governance framework, and security-focused culture.
[Download the whitepaper: 3DEXPERIENCE Cloud Security & Privacy](https://www.3ds.com/assets/invest/2025-04/3ds-whitepaper-cloud-security-privacy.pdf)
[Download the whitepaper: 3DEXPERIENCE Application Security](https://www.3ds.com/assets/invest/2025-05/3ds-whitepaper-application-security.pdf)
## Incident Response Team
The Computer Security Incident Response Team for Dassault Systèmes and its subsidiaries (3DS CSIRT) prevents, detects, and responds to cyber threats and incidents across all company assets. We take a proactive approach through continuous threat monitoring, vulnerability management, and NIST-aligned protocols.
Existing Dassault Systèmes customers are expected to use the support portal to report any issues, including security incidents, for any product or service through
[Download our RFC 2350-compliant CSIRT profile](https://www.3ds.com/assets/invest/2024-01/3ds-csirt-rfc2350.pdf)
View certificates in Security Resources
## Shared Responsibility in the Cloud
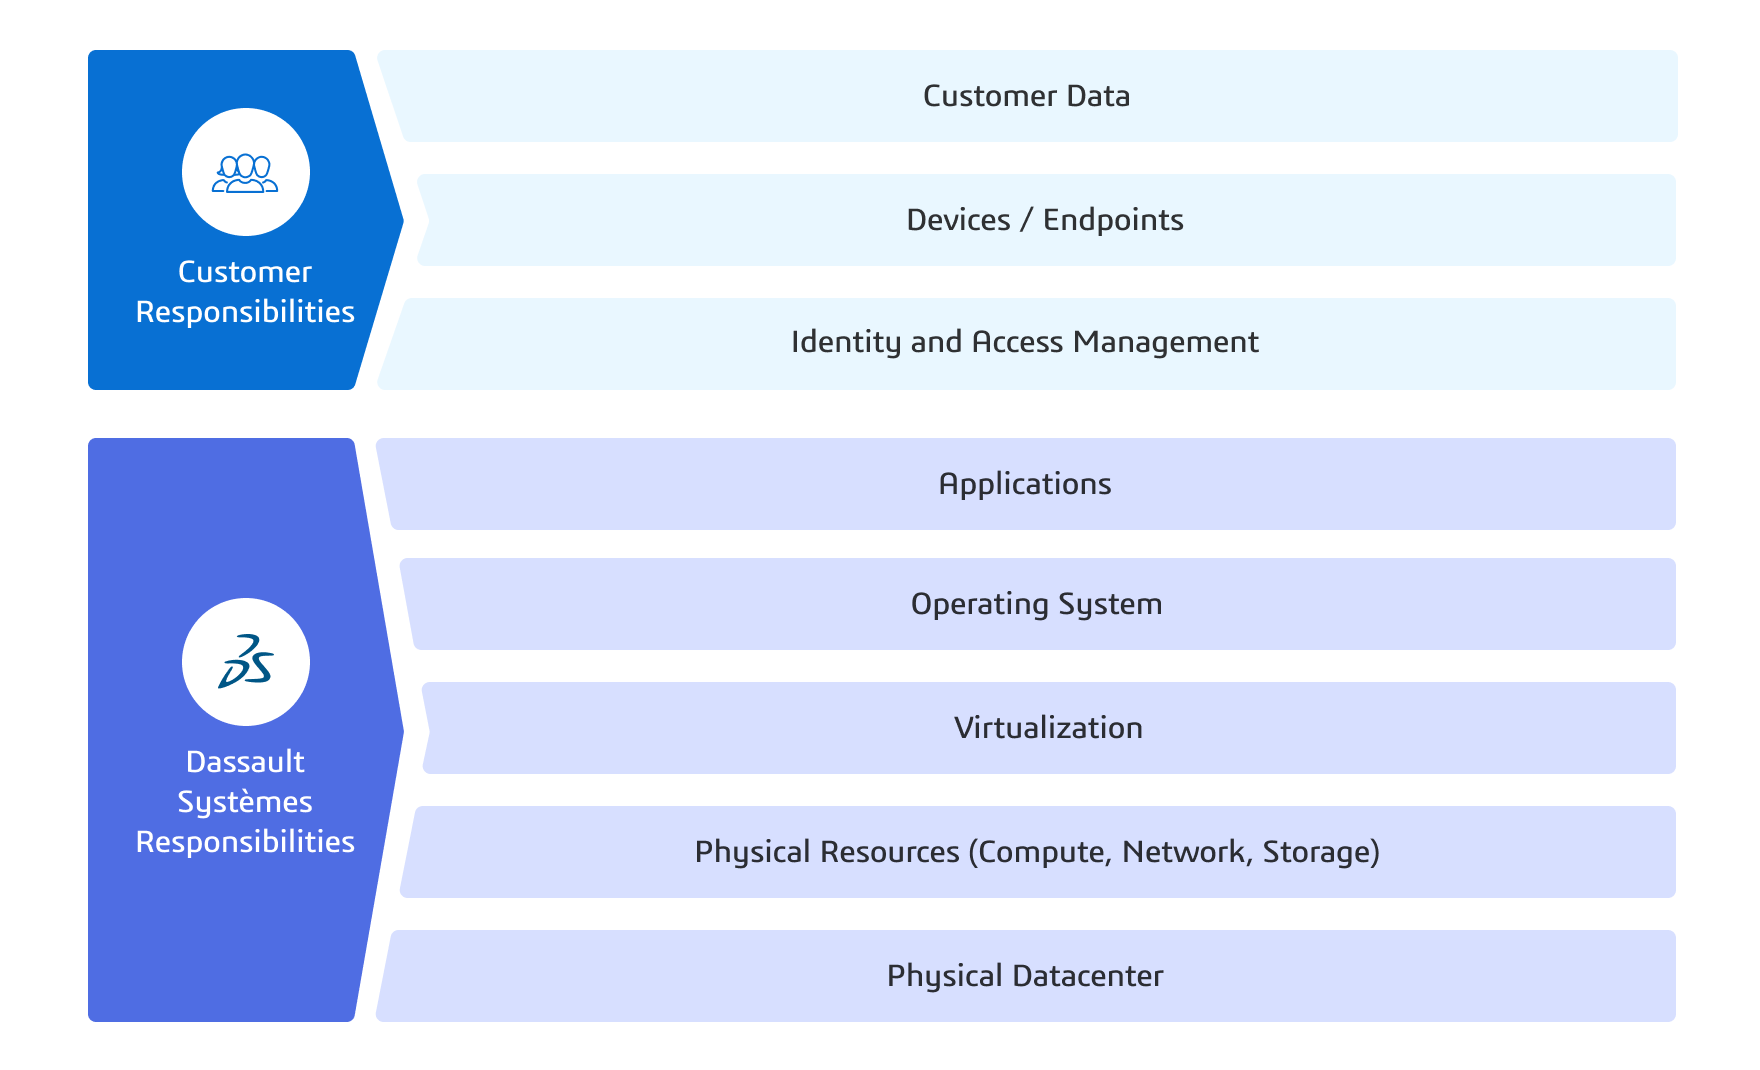
Our Shared Responsibility Model defines the division of responsibilities for security and compliance between Dassault Systèmes and our customers.
## Shared Responsibility Model
[](https://www.3ds.com/assets/invest/2025-02/shared-responsibility-model4.png)
## Infographic description
**Customer responsibilities:**
- Customer data
- Devices/Endpoints
- Identity and access management
**Dassault Systèmes responsibilities**:
- Applications
- Operating system
- Virtualization
- Physical resources (Compute, Network, Storage)
- Physical datacenter
[ Learn more about our Shared Responsibility Model ](https://assets.3ds.com/Terms/Shared%20Responsibility%20Model/3DS_Shared_Responsibility_Model_for_Online_Services_V1.1_July_2024.pdf)
## Vulnerability Testing
To stay ahead of evolving threats, we deploy Static and Dynamic Application Security Testing (SAST and DAST), Software Composition Analysis (SCA), penetration testing, and bug bounty programs. OWASP-aligned controls help ensure new security measures are continuously added.
## Penetration Tests
To help identify vulnerabilities and continuously improve our defense strategies, we regularly commission third-party cybersecurity professionals to simulate attacks on our solutions.
[View pentest assessments in Security Resources](#Brick-6da13b4a-15b9-464f-a62b-41cbb5111934)
## Private Bug Bounty Program
We invite ethical hackers to participate in a private bug bounty program to identify potential vulnerabilities in our cloud solutions and services.
## Vulnerability Reporting and Security Advisories
We welcome responsible vulnerability reporting from all parties, and we publicly disclose confirmed security issues affecting our products and services.
## Vulnerability Reporting
Vulnerability reporting is key to our security program. We welcome reports from security researchers to help us address potential issues while maintaining confidentiality and adhering to legal and ethical standards.
[ Review the reporting process](/trust-center/security/vulnerability-reporting)
## Security Advisories
Confirmed vulnerabilities in our solutions are published on the Security Advisories page, including CVE IDs, severity levels, affected versions, and remediation guidance, in alignment with MITRE CNA policies.
[Access our security advisories](/trust-center/security/security-advisories)
## Security Resources
Review our security-related certificates, assessments and whitepapers.
## Certificates & Reports
## ISO/IEC 27001:2022 Certified ISMS for Dassault Systèmes IT
The Information Security Management System for Dassault Systèmes Information Technology & Information Systems is certified to ISO/IEC 27001:2022.
Dassault Systèmes IT
[Download the certificate](https://www.3ds.com/assets/invest/2024-08/dassault-systemes-iso-iec-27001-2022.pdf)
## ISO/IEC 27001:2022 Certified ISMS for 3DEXPERIENCE platform SaaS
The Information Security Management System for the **3D**EXPERIENCE platform on the cloud is certified to ISO/IEC 27001:2022 for design, development, delivery, deployment, cloud operations and support.
3DEXPERIENCE platform
[Download the certificate](https://www.3ds.com/assets/invest/2025-01/dassaultsystemes-ios-eoc-27001-2022.pdf)
## ISO/IEC 27017:2015 Certified Cloud Security Controls for the 3DEXPERIENCE platform SaaS
The Information Security Management System for the **3D**EXPERIENCE platform on the cloud is certified for information security controls applicable to the provision and use of cloud services.
3DEXPERIENCE platform
[Download the certificate](/media/23979)
## CSA STAR Level 1 for 3DEXPERIENCE platform SaaS
**3D**EXPERIENCE platform SaaS is registered at STAR Level 1 in the cloud security alliance (CSA) Security, Trust, Assurance, and Risk (STAR) program. This program encompasses the key principles of transparency, rigorous auditing, and harmonization of standards.
3DEXPERIENCE platform
[Access the registry](https://cloudsecurityalliance.org/star/registry/dassault-systemes/services/3dexperience-platform-saas)
## The Italian National Cybersecurity Agency certified 3DEXPERIENCE platform SaaS
The Italian National Cybersecurity Agency (ACN) delivers QC1 qualification to the **3D**EXPERIENCE platform SaaS for the collaborative management of data, processes, simulations, and digital twins.
3DEXPERIENCE platform
[Access the registry](https://www.acn.gov.it/portale/en/w/sa-7759)
## ISO/IEC 27001:2022 Certified ISMS for DELMIA Hosted Solutions
The Information Security Management System for DELMIA Hosted Solutions, including operational, security, development and delivery processes, is certified to ISO/IEC 27001:2022.
DELMIA HOSTED SOLUTIONS
[Download the certificate](https://www.3ds.com/assets/invest/2025-03/delmia-dhs-iso-iec-27001-2022.pdf)
## ISO/IEC 27001:2022 Certified ISMS for DELMIAWorks Hosted Managed Services
The Information Security Management System for DELMIAWorks access controls and information assets and DELMIAWorks Hosted Managed Services (HMS) is certified to ISO/IEC 27001:2022.
DELMIAWorks
[Download the certificate](/media/23547)
## ISO/IEC 27001:2022 Certified ISMS for BIOVIA ScienceCloud
The Information Security Management System for the BIOVIA ScienceCloud platform, including security and operational business processes to support and manage the platform, is certified to ISO/IEC 27001:2022.
BIOVIA SCIENCECLOUD
[Download the certificate](https://www.3ds.com/assets/invest/2025-03/biovia-sciencecloud-iso-iec-27001-2022.pdf)
## ISO/IEC 27001:2022 Certified ISMS for Tuleap solution
The Information Security Management System of Enalean including software development, support and operations activities is certified to ISO/IEC 27001:2022.
CATIA Portfolio
[Download the certificate](/media/24552)
## SOC 2 Report for 3DEXPERIENCE platform SaaS
The management system over the **3D**EXPERIENCE platform on the Cloud has been independently audited by Deloitte under AICPA SOC 2 Type 2 standards, demonstrating effective controls for the trust service criteria relevant to security.
***Contact your account executive to request the report.***
3DEXPERIENCE PLATFORM
## SOC 2 Report for BIOVIA ScienceCloud
The Information Security Management System for BIOVIA ScienceCloud was independently audited under AICPA SOC 2 Type 2 standards, demonstrating effective controls for security, availability, and confidentiality.
***Contact your account executive to request the report.***
BIOVIA SCIENCECLOUD
## Trusted Information Security Assessment Exchange \[TISAX®\] Certified
The following sites are TISAX-certified with an AL3 level of assurance for information security and data protection: Darmstadt, Den Bosch, Detroit, Düsseldorf, Gilching, Krakow, Kuala Lumpur, Munich, Pune DSGS, Pune DSSL, Stuttgart, and Warwick.
TRANSPORTATION & MOBILITY
[Register to access](https://portal.enx.com/en-US/TISAX/tisaxassessmentresults/)
## SOC 2 Report for DELMIA Hosted Solutions
The Information Security Management System for DELMIA Hosted Solutions was independently audited under AICPA SOC 2 Type 2 standards, demonstrating effective controls for security, availability, and confidentiality.
***Contact your account executive to request the report.***
DELMIA HOSTED SOLUTIONS
## Dassault Systèmes UK Ltd has obtained Cyber Essentials certification
Dassault Systèmes UK Ltd has been certified as per the UK government Cyber Essentials scheme demonstrating it has put a core set of technical controls in place to defend against common cyber attacks.
Dassault Systèmes UK limited
[Download the certificate](/media/25362)
## PenTest Assessments
## R2026xGA Security Assessment
Third-party security assessment.
3DEXPERIENCE PLATFORM
[Download the certificate](https://www.3ds.com/assets/invest/2025-11/3dexperience-platform-security-assessment-2026x.pdf)
## R2025xGA Security Assessment
Third-party security assessment.
3DEXPERIENCE PLATFORM
[Download the certificate](https://www.3ds.com/assets/invest/2024-11/3dexperience-platform-security-assessment-2025x.pdf)
## R2025xGA Security Assessment - China
Security assessment conducted by the China National Quality Inspection and Testing Center for Cyber and Information System Security Products.
3DEXPERIENCE platform
[Download the certificate (Chinese only)](/media/24361)
## R2024xGA Security Assessment
Third-party security assessment.
3DEXPERIENCE PLATFORM
[Download the certificate](https://www.3ds.com/assets/invest/2023-11/3dexperience-platform-security-assessment-2024x.pdf)
## R2023xGA Security Assessment
Third-party security assessment.
3DEXPERIENCE PLATFORM
[Download the certificate](https://www.3ds.com/assets/invest/2022-12/3DEXPERIENCE_Plateform_Security_Assessment_R2023xGA.pdf)
## R2022x Security Assessment
Third-party security assessment.
3DEXPERIENCE PLATFORM
[Download the certificate](https://www.3ds.com/assets/invest/2022-08/3dexperience-platform-security-assessment-2022x.pdf)
## BIOVIA ScienceCloud Security Assessment
Third-party security assessment.
BIOVIA SCIENCECLOUD
[Download the assessment](https://www.3ds.com/assets/invest/2025-04/biovia-sciencecloud-audit-attestation-of-security.pdf)
## SIMULIA Wave6 Release 2026 Golden Security Assessment
Third-party security assessment.
SIMULIA Portfolio
[Download the certificate](https://www.3ds.com/assets/invest/2026-04/simulia-wave6-security-assessment-2026.pdf)
## SIMULIA Simpack Release 2026x\_Refresh2 Security Assessment
Third-party security assessment.
SIMULIA Portfolio
[ Download the certificate](https://www.3ds.com/assets/invest/2026-04/simulia-simpack-security-assessment-2026x.pdf)
## SIMULIA Tosca for Abaqus Release 2026 Golden Security Assessment
Third-party security assessment.
SIMULIA Portfolio
[Download the certificate](https://www.3ds.com/assets/invest/2026-04/simulia-tosca-security-assessment-2026.pdf)
## SIMULIA Abaqus Release 2026 Golden Security Assessment
Third-party security assessment for Abaqus/CAE and Abaqus/Viewer.
SIMULIA Portfolio
[Download the certificate](https://www.3ds.com/assets/invest/2026-04/simulia-abaqus-security-assessment-2026.pdf)
## Security Whitepapers
## Cloud Security & Privacy Whitepaper
We operate a comprehensive ISMS certified to ISO/IEC 27001 and 27701, supported by a SSDLC, multi-layer vulnerability management, NIST-based incident response, and a shared responsibility model.
3DEXPERIENCE PLATFORM
[Download the whitepaper](https://www.3ds.com/assets/invest/2025-04/3ds-whitepaper-cloud-security-privacy.pdf)
## Application Security Whitepaper
For application security, our SSDLC integrates OWASP, NIST SP 800-53, and ISO/IEC 27001 standards, MFA, auditing, SAST/DAST scanning, penetration testing, and more.
3DEXPERIENCE PLATFORM
[Download the whitepaper](https://www.3ds.com/assets/invest/2025-05/3ds-whitepaper-application-security.pdf)
## Cloud Security Whitepaper
Our ScienceCloud security team operates a SSDLC, ISO/IEC 27001-certified ISMS, SIEM-driven threat detection, DLP, HIDS/HIPS, MFA, role-based access control, continuous vulnerability scanning (SAST/DAST), and incident response aligned to NIST and CSA CCM standards.
BIOVIA SCIENCECLOUD
[Download the whitepaper](https://www.3ds.com/assets/invest/2025-03/biovia-science-cloud-security-datasheet-en.pdf)